
In cybersecurity, six professionals can sit in the same room, discuss the same security problem, and describe it in six completely different ways.
Each role has its own priorities, terminology, and approach to finding solutions.
For instance, A CISO prioritizes enterprise risk exposure and the business impact of identity-related breaches. Conversely, an IAM administrator focuses on operational controls such as automating user deprovisioning and managing access permissions.
Both work in identity security, yet their responsibilities differ entirely. That also means the content they consume also differs.
This creates a major SEO problem most cybersecurity vendors underestimate.
The keyword strategies that work in traditional B2B don’t apply here, because there is no single shared vocabulary to optimise around.
Building a universal page for every persona creates vague content that speaks to no one. The result is typically an instant bounce, since that persona couldn’t find what they were looking for.
And once they bounce, they might never return.
This post explains why cybersecurity terminology fragments, how to map keywords to personas instead of categories, and when to use analyst-coined terms versus operational language. If you are new to the topic, start with our pillar guide on cybersecurity SEO here. If you’re already familiar with the basics, keep reading.
What you will learn:
- Why different cybersecurity professionals use different search terms for similar security challenges.
- How IAM administrators, CISOs, and developers approach identity security differently.
- How to map keywords to the needs and language of each buyer persona.
- Why keyword strategies should focus on real search demand rather than industry jargon.
Why cybersecurity terminology mapping differs by persona
From a marketing perspective, “identity security” may seem like a single topic. But within a security team, different roles approach it from different angles, each with distinct priorities, challenges, and specific terminology.
Content that satisfies one persona’s search intent might completely miss the mark for another.
- An IAM administrator working on day-to-day identity infrastructure thinks about access reviews, lifecycle automation, joiner-mover-leaver workflows, and policy enforcement. Their language is operational and tool-specific.
- A CISO prioritizes business risk and threat exposure. They’re responsible for reducing identity-related risk, ensuring effective identity governance, and maintaining audit readiness. Their language is strategic and business-focused.
- A developer approaches identity from a technical, implementation-driven perspective. They focus on securing service account credentials, managing OpenID Connect (OIDC) tokens, and rotating machine identity credentials. Their language is highly technical and closely tied to code and development workflows.
All three personas have a shared interest in “identity security”, but they’re asking different questions, using different terminology, and looking for different answers.
Creating a generic glossary page can’t address those specific areas.
A terminology map does.
The three-column terminology map
A three-column terminology map lists the actual search terms each cybersecurity persona uses for a given concept. Mapping “identity security” across IAM admin, CISO, and developer personas reveals three distinct keyword sets, each with different intent.
A generic landing page will struggle to rank for any of them, while persona-targeted pages outperform consistently.
This is the most valuable exercise we’ve used in our cybersecurity marketing work with clients.
For each major concept the company offers, we map the actual search terms those unique personas use. The three-column comparison table below shows how specific keyword sets map to distinct security persona search terms.
| IAM administrator | CISO | Developer |
|---|---|---|
| Conditional access policy drift | Identity attack surface | Service account secrets management |
| Okta lifecycle automation | Identity threat visibility | OIDC token compromise |
| Identity governance provisioning | Identity risk reduction | Machine identity rotation |
| Privileged access review | Identity blast radius | Workload identity federation |
| Access certification campaigns | Identity-driven breach exposure | SDK authentication patterns |
All five rows address the same underlying problem, but the searches map to three completely different intent profiles. A generic glossary page covering “identity security” will struggle to rank for any of these personas, and will most likely not result in any conversions.
So then, what’s a better strategy?
Persona-targeted depth.
A single page covering identity governance for IAM administrators. Another page covering identity risk reduction for CISOs. A third covering workload identity for developers. Each page targets a more specific set of terms, improving its chances of ranking for relevant searches and converting visitors by matching their search intent.
And there’s even more incentive to create them.
McKinsey found that persona-based marketing can boost revenues by 5-15% and increase marketing ROI by 10-30% on average.
How to map cybersecurity SEO keywords to personas, not categories
To map cybersecurity keywords to personas rather than product categories, start by defining the three to five buyer personas you actually sell to. Interview representatives of each persona to capture their real vocabulary, map their terminology to commercially relevant content topics, and create persona-specific pages instead of relying on generic messaging.
Topical authority compounds faster when each page goes deeper on a narrower vocabulary.
The standard B2B SEO playbook starts with a category map: features, use cases, integrations, and comparison pages. That works in horizontal SaaS, where most buyers describe products in similar language.
It differs in cybersecurity, where the same product solves different problems for different personas.
We’ve outlined a 4-step cybersecurity keyword strategy below:
Step 1: Define the three to five personas you actually sell to. Most cybersecurity vendors sell to more personas than they realise. A typical EDR vendor might sell to SOC analysts (technical evaluators), security engineers (implementation and integration owners), CISOs (budget holders), and GRC leaders (regulatory requirements and audit readiness).
Each persona has a distinct vocabulary and search when comparing EDR solutions. Each destination page should address those persona questions specifically.
Step 2: Interview each persona about their actual language. Pull language from sales call recordings, customer interviews, support tickets, and community forum discussions. Study the terms and questions your buyers actually use, rather than the language your product marketing team prefers.
You’ll uncover persona-specific vocabulary, recurring pain points, and search queries that traditional keyword research might miss.
Those recurring pain points eventually become helpful technical guides, comparison pages, implementation playbooks, troubleshooting tutorials, configuration checklists, integration documentation, ROI calculators, and interactive product demos. Each is focused on a specific persona.
| 💡Wadi Tip: Upload all of the recordings and interview transcripts into Claude or ChatGPT and ask it to give you lists of persona-specific keywords, phrases, and topics. |
Step 3: Map the terminology to commercially relevant content topics. Each persona’s vocabulary maps to a different set of search intents. IAM administrators search for implementation documents. CISOs search for risk frameworks. Developers search for SDKs and API integrations. The content you create should reflect those unique challenges.
Step 4: Search Reddit for relevant phrases and common questions from cyber-specific personas.
| Reddit ranks #1 in the US for estimated SEO traffic per month, with 858.2M searches |
Reddit is exceptionally valuable for finding technical questions and terms asked by potential cyber buyers. Reddit is also a goldmine of content ideas. Pay close attention to trending threads with lots of comments. Turn these topics into persona-specific content pieces, such as customer-facing assets, sales materials, and other content that addresses the challenges each persona actually cares about.
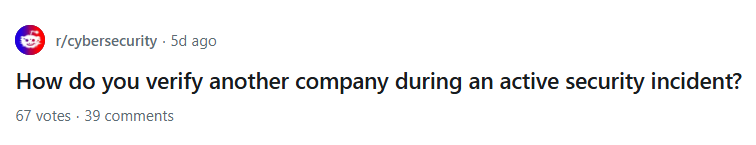
For example, a recurring question about SIEM costs could become a cost-optimization guide for CISOs, a technical tutorial for SOC analysts, and a sales battlecard highlighting how your solution compares to alternatives.
One topic. Multiple personas. Different content assets.
| 💡Wadi Tip: Check out these industry-specific cybersecurity subreddits for long-tail keywords and unique search terms from specific personas. |
When to use analyst-coined terms versus operational language
Use analyst-coined terms (CNAPP, DSPM, ITDR, CTEM, AISPM) when keyword research shows real organic search demand.
Use operational language when analyst terms have industry momentum but no proven search behaviour yet. New analyst categories often lag actual search demand by 12 to 24 months, and conference visibility rarely translates to search volume on the same timeline.
Cybersecurity vendors often prioritize category terms promoted by Gartner, Forrester, and investor decks.
These terms may gain industry momentum before meaningful search demand develops. While analyst-driven terminology signals that the market is paying attention to a concept, buyers may not yet be searching for it by name. Instead, they’re searching for the problems it solves.
We see stronger SEO performance from practical implementation terminology than from emerging category branding alone.
For example, “cloud misconfiguration detection” may attract more search demand than “CNAPP posture optimization,” depending on the market’s maturity. Buyers searching for a specific operational problem may significantly outnumber those searching for the analyst-defined category, sometimes by an order of magnitude.
A common pattern we’ve observed:
- An analyst coins a term
- Vendors adopt it for category positioning
- Search demand catches up 12 to 24 months later, sometimes longer
- During the gap, content optimised for the new term struggles, while content optimised for the underlying operational problem performs
The rule we apply with clients is simple.
Use analyst-coined terms when search demand actually exists (this can be verified in any keyword tool). Use operational language when the analyst term has industry momentum but no organic search behaviour yet. Conference visibility doesn’t translate into search volume since industry awareness and search demand evolve on different timelines.
How to define cybersecurity terminology inline without losing readers
Define technical cybersecurity terms on first use with a short parenthetical explanation. For example: “DSPM (Data Security Posture Management) identifies and prioritises data risks across cloud environments.” The long-tail keyword expansion helps less-familiar readers understand the term while reinforcing the keyword for search engines.
Don’t assume everyone knows the acronyms.
CISOs and cloud solution architects most likely know what a CNAPP (Cloud-Native Application Protection Platform) means. Board members and non-technical decision-makers might not. If readers have to decode your terminology before they can understand your point, you risk losing them in the first paragraph.
And once again, this translates into an instant bounce on your site.
Summing it all up…
The goal of terminology mapping isn’t to simplify the cybersecurity language itself, but to make complex topics more navigable without flattening technical credibility.
This is the fine balance you need to strike when speaking to different buyers.
Want a persona-mapped cybersecurity SEO strategy that actually matches how your buyers search?
Book a 30-minute strategy session with our team.
Key takeaways
- Cybersecurity terminology mapping differs by persona, not just by category. IAM admins, CISOs, and developers describe the same concept in completely different language.
- A generic glossary page will struggle to rank for all personas.
- Persona-targeted depth outperforms blended content in cybersecurity SEO.
- Build a terminology map for each major concept you sell around, then create persona-specific content tracks for each.
- Analyst-coined terms (CNAPP, DSPM, ITDR) often carry industry momentum but lag in actual search demand by 12 to 24 months.
- Define acronyms inline on first use. The benefit to less-familiar readers and search engines is significant.
FAQs
How many cybersecurity personas should I map for SEO?
Most cybersecurity vendors should map between three and five personas. Common splits include SOC analyst, security engineer, CISO, and CFO. The right number depends on which personas actually influence the buying decision in your specific category. More than five usually dilutes content production capacity.
Should I optimise for analyst-coined category terms like DSPM or CTEM?
Optimise for analyst-coined category terms only when keyword research shows real search demand. Many analyst-coined terms carry strong industry momentum but minimal organic search volume for 12 to 24 months after coining. During the gap, content optimised for the underlying operational problem (rather than the analyst category) usually performs better.
How do I find out which terms each cybersecurity persona actually uses?
The most reliable sources are sales call recordings, customer interviews, support ticket transcripts, and community forum discussions. Avoid relying solely on internal product marketing language, which often reflects vendor preferences rather than buyer vocabulary.
Can I cover multiple cybersecurity personas on one page?
You can mention multiple personas on one page, but trying to rank for all of their vocabularies simultaneously usually produces vague content that satisfies none of them. Persona-specific pages with deeper, narrower vocabulary consistently outperform blended pages in cybersecurity SEO.